Digital regulation in Australia: how new regulations converge and intersect
15 September 2026
The digital duty of care is the latest in a series of regulatory reforms impacting digital regulation in Australia. No reform can be viewed in isolation. The digital duty of care sits within a broader, evolving digital regulatory framework including the Privacy Act tranches, the Children’s Online Privacy Code, the Social Media Minimum Age and the artificial intelligence standards. Further details about each are discussed below.
Digital duty of care
The exposure draft of the Online Safety Amendment (Digital Duty of Care) Bill 2026 was released on 8 September 2026. If passed, the Bill would introduce a proactive, systems-based digital duty of care that would move beyond the Online Safety Act 2021 (Cth)’s current co-regulatory framework. It applies to every person 'responsible for' an 'online service'.
Privacy Act Tranche 2
The exposure draft was released in August 2026. Key proposals include a new ‘fair and reasonable’ test for the collection and use of personal information, strengthened consent standards, a statutory controller/processor framework, a right of erasure for large digital platforms, and enhanced data security obligations.
Children’s Online Privacy Code
To be registered in December 2026, the Code applies to providers of social media services, relevant electronic services and designated internet services (all defined by reference to the OSA) that are ‘likely to be accessed by children’. Key features will likely include stricter limits on the collection of children’s data, enhanced consent requirements, mandatory age assurance, a child-specific right of destruction, and mandatory privacy impact assessments.
Social Media Minimum Age
The SMMA has been in force since December 2025, requiring age-restricted social media platforms to take reasonable steps to prevent under-16s from having accounts. The OAIC has published guidance on data handling in this context, covering matters such as data minimisation, destruction-on-decision for age verification data, and ring-fenced processing environments that may be relevant to the digital duty of care’s design feature protections.
Artificial intelligence standards
In July 2026, the Prime Minister announced a shift from voluntary guidance to mandatory national regulation for AI, including mandatory standards for large AI data centres, copyright protections for Australian creators, and AI consumer safety requirements. An Office of AI has been established within the Department of the Prime Minister and Cabinet, with legislation expected in early 2027.
How Australia’s digital regulation overlaps
The below illustrates where Online Safety obligations meet Privacy Act reforms, and maps the timeline and convergence of Australia's digital regulatory landscape.
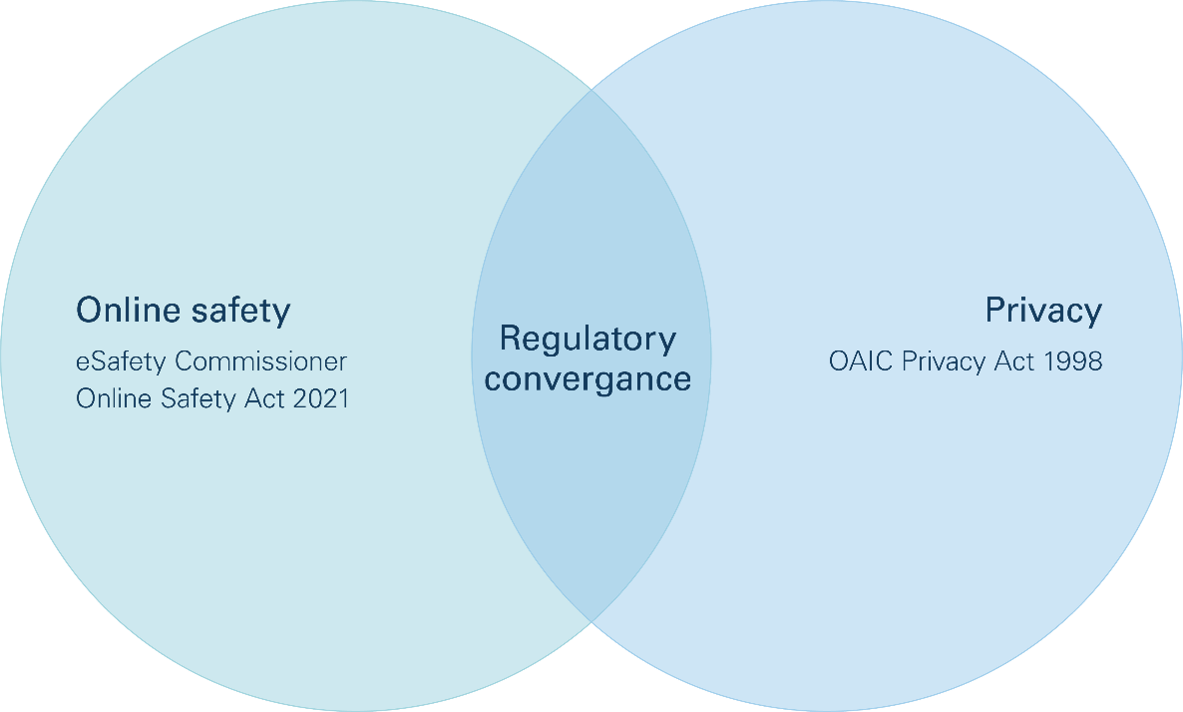
| Timing | Online safety reforms | Crossover | Privacy Act reforms |
|---|---|---|---|
| December 2024 | Privacy Act – Tranche 1 reforms (in force) The first legislative response to the 2023 Privacy Act Review Report. Introduced: anti-doxxing offences; automated decision-making transparency requirements, new civil penalty tiers, strengthened OAIC enforcement powers, requirement for a Children’s Online Privacy Code. | ||
| June 2025 | Statutory tort for serious invasions of privacy commences (in force) Not limited to APP entities – a cause of action can be pursued against any person or organisation. | ||
| December 2025 | Social media minimum age requirements (in force) Requires ‘age-restricted social media platforms’ to take ‘reasonable steps’ to prevent under 16s having accounts. The changes impose specific rules on age-restricted social media platforms regarding how they handle data collected for age verification purposes. These rules apply alongside Privacy Act obligations. | Platforms must comply with specific rules on handling data collected for age verification purposes. These rules apply alongside Privacy Act obligations and are partly enforced by the OAIC. | |
| March 2026 | Age-Restricted Material Codes come into effect (in force) Require providers of designated internet services and relevant electronic services to take steps to prevent children from accessing age-restricted material (e.g. pornography), including through age assurance mechanisms. | Children's Online Privacy Code – exposure draft released (proposed) The OAIC publishes the exposure draft Code, which applies to providers of social media services, relevant electronic services or designated internet services (all defined by reference to the Online Safety Act) that are 'likely to be accessed by children'. Key features include stricter limits on collection of children's data, enhanced consent requirements (parental consent for under-15s), mandatory age assurance, a child-specific right of destruction, and mandatory privacy impact assessments. Consultation closed 5 June 2026. | |
| April 2026 | Online Safety Act Review - government response Government supports 64 of 67 recommendations from the independent statutory review, with a digital duty of care as the headline commitment alongside stronger accountability and enforcement measures for digital platforms. | ||
| July 2026 | Australian standards for AI announced (proposed) PM announces shift from voluntary guidance to mandatory national regulation. A single national framework will set mandatory standards for large AI data centres (energy, water, community impact), copyright protections for Australian creators, and AI consumer safety priorities. Office of AI established within PM&C. Legislation expected early 2027. | ||
| August 2026 | The Privacy Act refers to the Online Safety Act to define 'large digital platforms’ The right of erasure applies to providers of social media services, relevant electronic services or designated internet services (as defined in the Online Safety Act) that meet a $500 million group revenue threshold or have 2.5 million average monthly Australian end users. | Privacy Act – Tranche 2 reforms – exposure draft released (proposed) Proposes a new 'fair and reasonable' test for the collection and use of personal information (replacing APPs 3, 4 and 6); stronger consent standards (voluntary, informed, current, specific and unambiguous); a statutory controller/processor framework; restrictions on the trading of personal data; a right of erasure targeting large digital platforms; a hard 72-hour data breach notification deadline; and enhanced data security obligations. Submissions close 18 September 2026. | |
| September 2026 | Digital Duty of Care – exposure draft released (proposed) Applies to persons responsible for 'online services' (including social media, messaging, websites, app stores, search engines, ISPs, hosting services, and AI content generation services). Services must ensure, 'so far as is reasonably practicable', a 'safe online environment'. Key obligations include managing design features, conducting annual risk assessments, and three tiers of protection escalating from all Australians to children under 18 to children under 16 on social media. Civil penalties of up to ~$109.2 million for bodies corporate. 12-month transition after Royal Assent. | A person responsible for an online service would need to ensure, ‘so far as is reasonably practicable’, a ‘safe online environment’. The test builds in an express privacy safeguard – requires consideration of whether a safety measure’s impact on privacy is ‘grossly disproportionate’ to the risk being addressed. | |
| September 2026 | Consultation on proposed digital duty of care closes (22 September) | Consultation on Tranche 2 reforms closes (18 September) | |
| December 2026 | Children's Online Privacy Code to be registered (proposed – effective date TBC, likely with transitional period) and ADM transparency requirements come into force | ||
Authors
Head of Technology, Media and Telecommunications
Partner
Head of Intellectual Property
Special Counsel
Senior Associate
Associate
Associate
Associate (Admitted in England & Wales, not admitted in Australia)
Lawyer
Tags
This publication is introductory in nature. Its content is current at the date of publication. It does not constitute legal advice and should not be relied upon as such. You should always obtain legal advice based on your specific circumstances before taking any action relating to matters covered by this publication. Some information may have been obtained from external sources, and we cannot guarantee the accuracy or currency of any such information.
Contacts